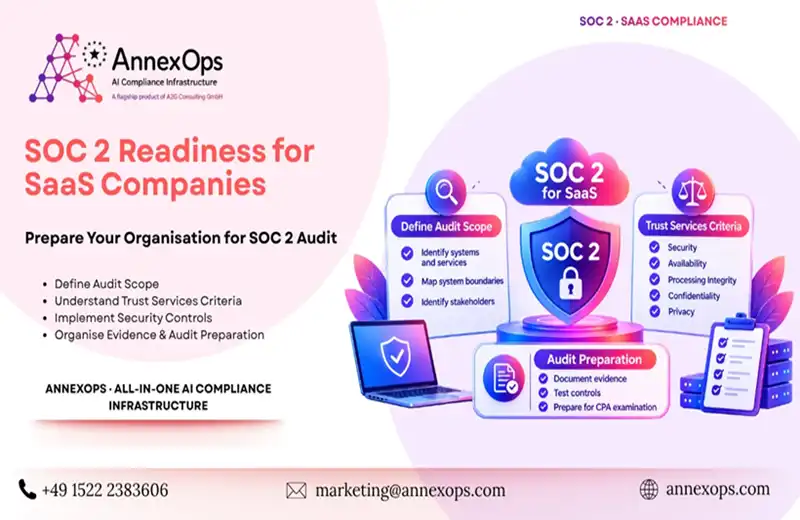
Winning enterprise customers takes more than a great SaaS product. Buyers want confidence that your company protects sensitive data, manages security risks and maintains reliable internal controls. This makes SOC 2 readiness for SaaS companies an important step towards building customer trust and meeting enterprise security expectations.
This guide covers the essential steps of SOC 2 preparation, including audit scope, Trust Services Criteria, control implementation, vendor risk management, evidence collection and Type 1 vs Type 2 examinations. Learn how to identify control gaps, organise audit documentation and prepare your teams for the examination process.
AnnexOps helps SaaS businesses manage compliance documentation, control tracking and audit evidence through structured workflows.

 Australia
 India
 Singapore
 United Kingdom
 United States
 South Africa
 New Zealand
 Nigeria
 Canada
 France
 Spain
 Italy
 Ireland
 UAE

