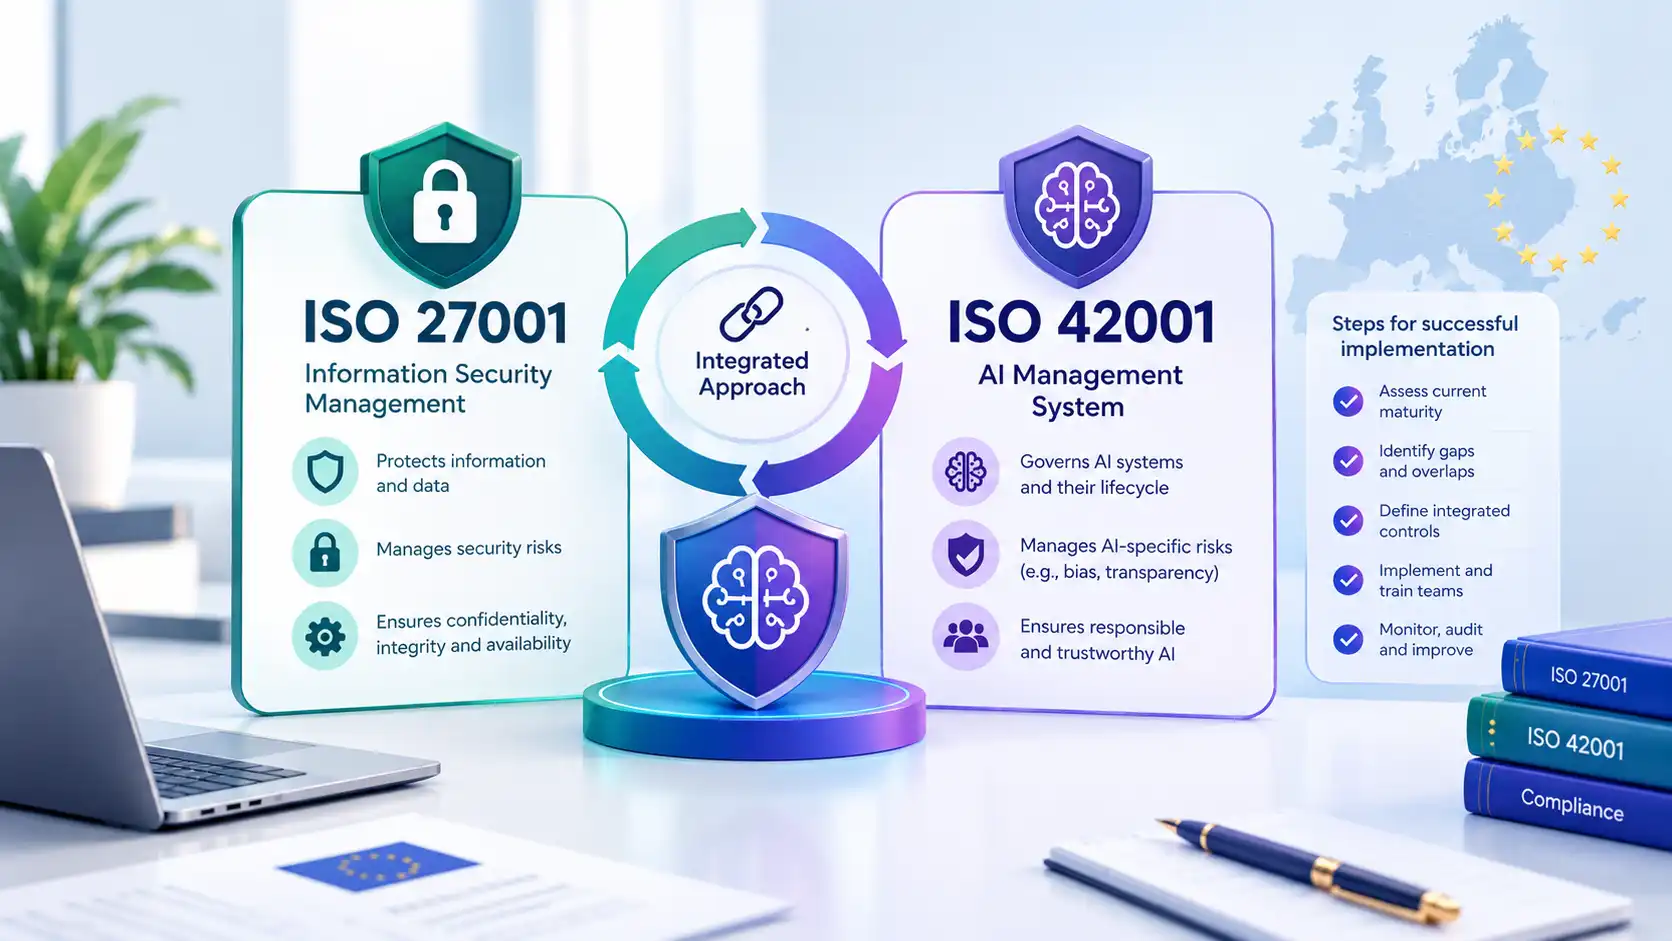
Already using ISO 27001 and planning to implement ISO 42001? Organisations can build on relevant information security processes while addressing AI-specific requirements, including AI risk assessment, impact assessment, governance, and lifecycle controls. Although both standards share a management-system structure, ISO 27001 certification does not automatically satisfy ISO 42001 requirements. This guide explains the implementation steps, identifies processes that may be reused, and highlights the additional work needed to establish an AI Management System. Discover how AnnexOps supports AI governance, documentation, risk management, and compliance evidence through connected workflows.

 Australia
 India
 Singapore
 United Kingdom
 United States
 South Africa
 New Zealand
 Nigeria
 Canada
 France
 Spain
 Italy
 Ireland
 UAE